Kovallent
Shift parameter contract enforcement left into git commit with kv-cli, and manage centralized policy, auditability, and team compliance in the Kovallent Control Plane.
 Apache Airflow
 PySpark
dbt Core / Cloud
 Polars
Delta Lake
Apache Iceberg
15 engineers writing pipelines 15 different ways — resulting in endless PR reviews and zero consistency.
Senior architects bogged down answering tribal knowledge questions for every new hire.
Pipelines breaking in production because dev, stage, and prod handle job arguments inconsistently.
Kovallent reads pipeline code directly through AST parsing — it doesn't connect tool-by-tool, so it works with any tech stack already in place. These are the layers that see the biggest payoff from that standardization:
Airflow
PySpark
Polars
 Snowflake
 Databricks
 BigQuery
Amazon EMR
Don't see your exact tools listed — if it's Python, SQL, or YAML living in a Git repo, Kovallent can parse it.
kv-cli is the open-source Rust binary that runs locally and in CI — parsing your Python pipeline code with tree-sitter and blocking the commit the moment a job breaks its parameter contract, hardcodes a secret, or pins itself to one environment.
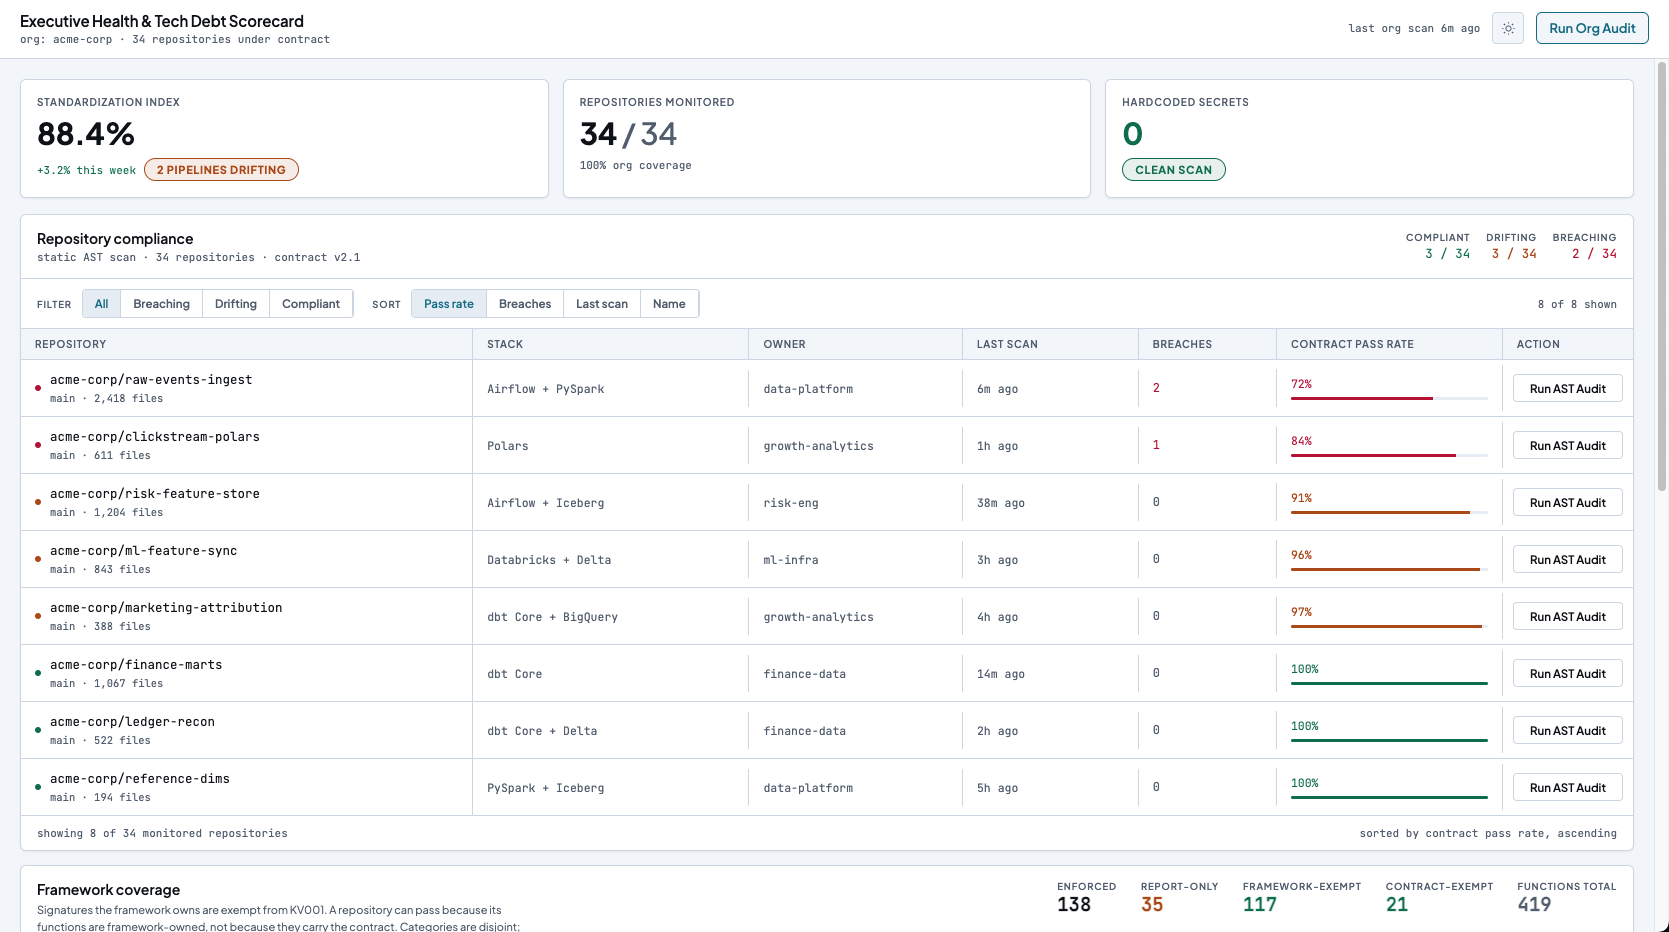
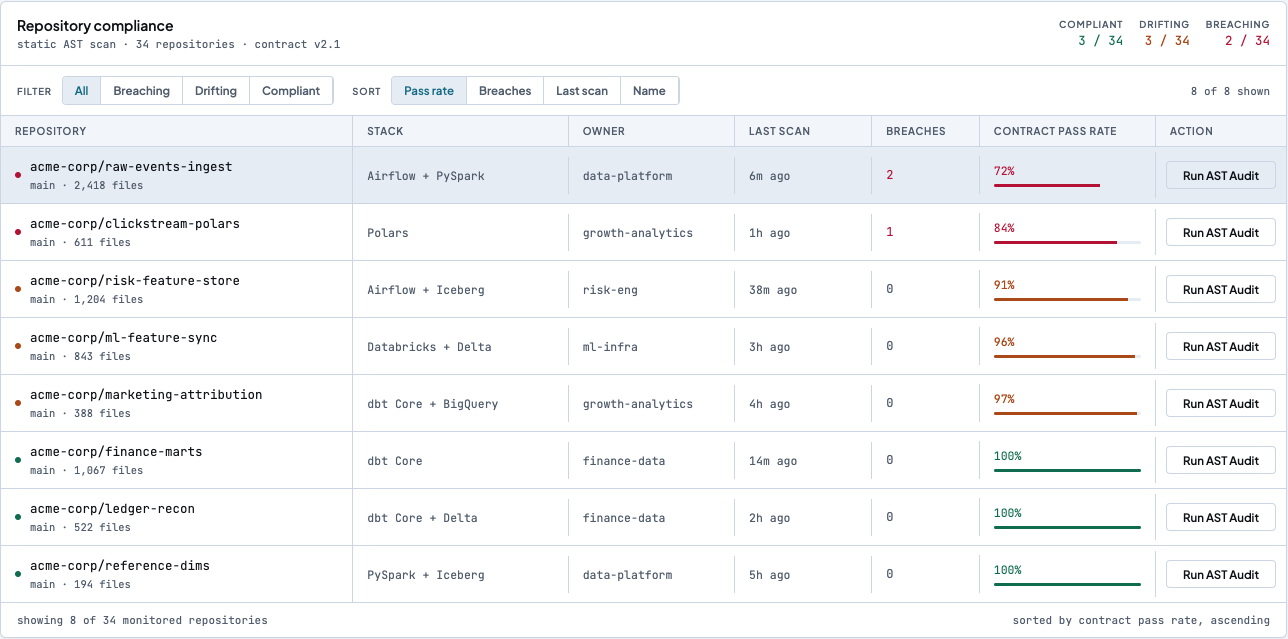
Engineering leads see all 34 monitored repositories at once — real-time stack tagging, last-scan timestamps, and one-click AST audit triggers — instead of checking each repo's CI logs individually.
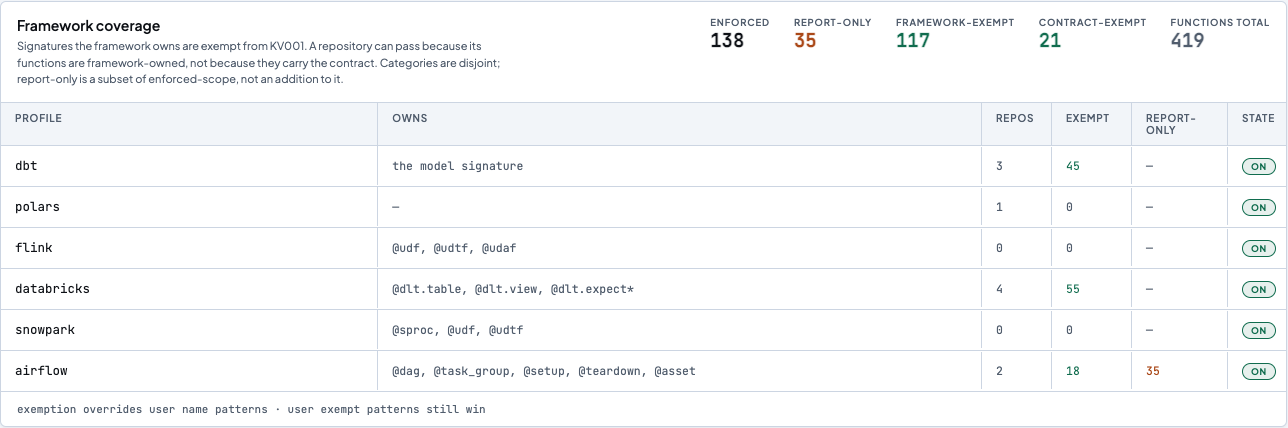
Exemptions are subtractive — a repo passes because dbt or Databricks explicitly owns that signature check, not because Kovallent quietly looked away. The Framework Coverage panel shows exactly which framework covers which check, so every passing result stays auditable.
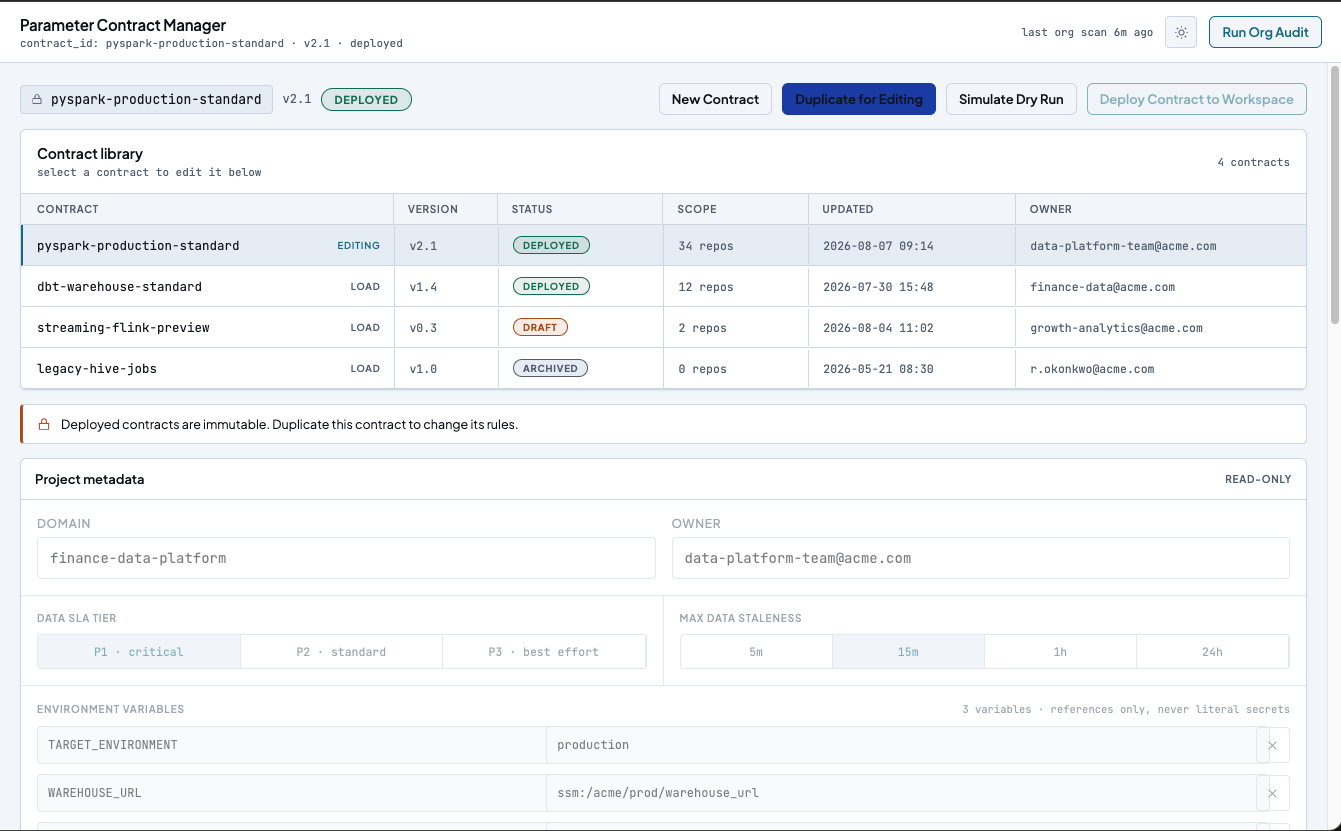
Create a parameter contract, version it, and deploy it. Deployed contracts are immutable — teams duplicate to iterate rather than quietly rewriting the rules underneath a pipeline that's already passing. One naming convention, enforced org-wide.
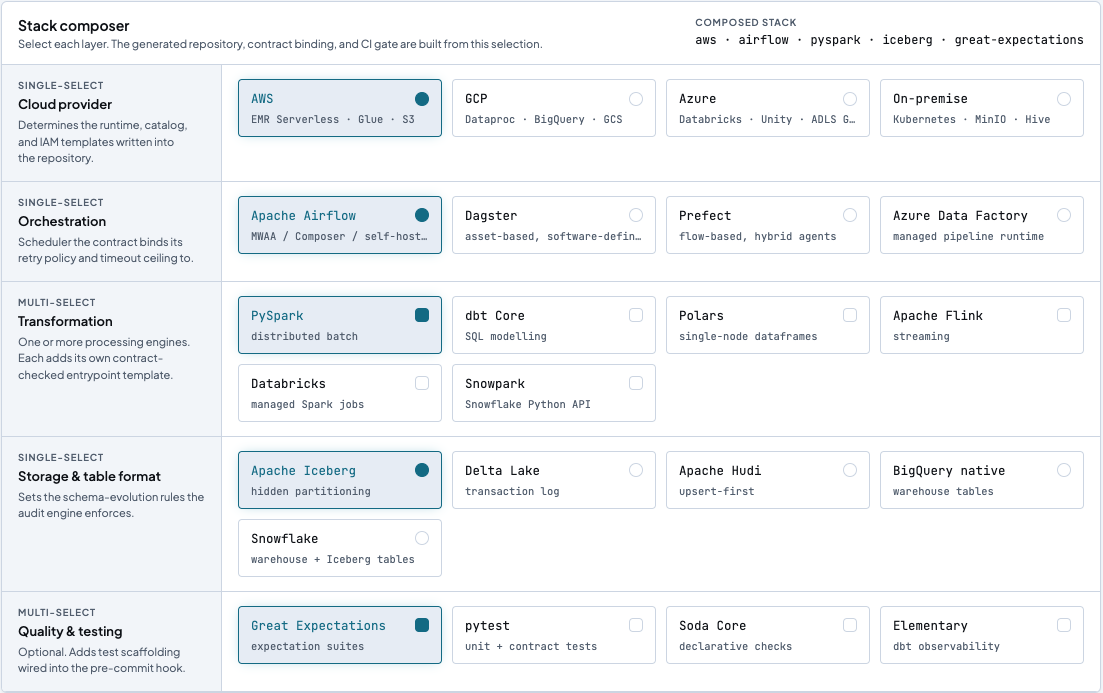
Compose a repository from your chosen cloud, orchestration, and transformation tools, and Scaffold Studio generates it with contracts and guardrails already installed. Security & Secrets scans every commit across every cloud provider and warehouse for hardcoded credentials before they ship.
Traditional data observability platforms tell you when your pipeline breaks — after the compute has run, after the bad data has landed in your warehouse, and after executives see corrupted dashboards.
Kovallent takes a fundamentally different approach. As the Shift-Left Data Engineering Control Plane, Kovallent intercepts bad code, parameter drift, and missing contract schemas in local IDEs and CI/CD pipelines — before non-compliant code ever merges into production.
| DIMENSION | Post-Execution Observability |
Kovallent Shift-Left |
|---|---|---|
| Core focus | Reactive anomaly detection | Proactive code guardrails |
| Execution layer | Runtime (post-database) | Local IDE & pre-commit CI/CD |
| Cloud compute cost | Pays for failed job runs | $0 compute wasted |
| Parse engine latency | Minutes to hours | <200ms AST local scan |
| Schema & parameter drift | Alerted after table breaks | Blocked before PR merges |
| Hardcoded secrets detection | Out of scope (data-at-rest) | Pre-commit git hook blocking |
| Production backfill effort | Days spent re-running DAGs | Zero (bad code never lands) |
Post-execution observability tools run continuous, resource-heavy queries against your data warehouses to detect anomaly spikes. You pay twice: once for the failed Spark/dbt job run, and again for the observability platform to query the corrupted tables.
Observability tools generate Slack alerts when schema drift breaks a pipeline. By the time your team receives the alert, downstream dashboards are out of date and your data team is forced into emergency backfill mode.
Fixing a schema error or unhandled parameter exception in production requires opening an incident, investigating root causes across complex lineage graphs, writing a hotfix, and running expensive backfills.

Read-only OAuth or token setup in under 60 seconds. No write access, ever.
We scan every repo against your enterprise design system contracts — dependencies, parameters, secrets.
View a live dashboard and export a board-ready PDF action plan.
Pay for the engineers actually pushing code — plus the repos you want monitored. Read-only viewers are always free.
| FEATURE | Developer | Team | Enterprise | Custom / Gov |
|---|---|---|---|---|
| Local kv-cli executions | Unlimited | Unlimited | Unlimited | Unlimited |
| Included monitored repos | 3 repos | 20 repos | 100 repos | Custom / unlimited |
| CI/CD quality gates | — | 5 pipelines | Unlimited | Unlimited |
| Parameter Contract Builder | Basic | Advanced | Custom schemas | Custom schemas |
| Scaffold Studio blueprints | — | — | Full access | Custom blueprints |
| Executive Health Scorecard | — | — | Included | Custom board reports |
| Authentication & SSO | GitHub OAuth | GitHub OAuth | SAML / Okta / Azure AD | SAML / Okta / custom OIDC |
| Deployment model | Local CLI | Multi-tenant cloud | Multi-tenant cloud | VPC / on-prem / air-gapped |
| Support SLA | Community | 24-hour email | 4-hour priority | 1-hour / 24-7 dedicated |
Any developer who opens a pull request or pushes code parsed by Kovallent in a 30-day window. Read-only managers and executives viewing scorecards do not require a seat license.
You will never be blocked unexpectedly. Enterprise accounts can add extra repository packs ($20/mo per 5 repos) or upgrade tiers directly from the workspace dashboard.
Yes. Kovallent's Cloud Audit Engine uses strictly read-only OAuth permissions to analyze code metadata and parameter signatures via Abstract Syntax Trees. We never alter code or access production data rows.
Two-minute scan. Zero write access. One scorecard your board will actually read.
Join Waitlist